Read each change
with the code around it.
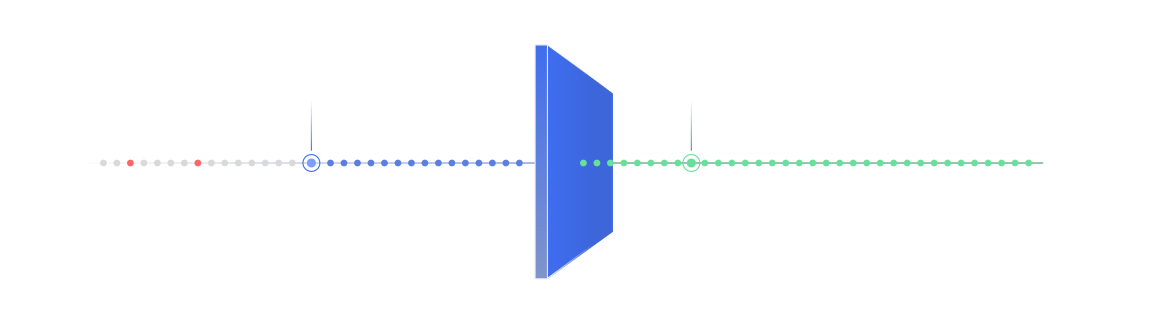
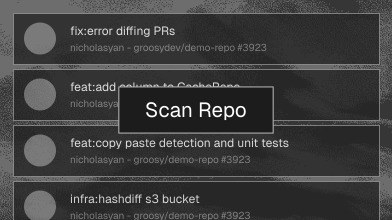
Goosy reads the changed lines and the code that calls them. Deep Scan covers the whole repository on demand or on a daily schedule.
Goosy reviews every pull request and scans your whole repository for vulnerabilities and bugs. Every finding points to the exact lines and explains why it matters.
Works with GitHub, GitLab and MCP clients such as Claude Code, Cursor and VS Code
HOW IT WORKS
Four steps, from a connected repo to a fix you approve.
Less noise reaches you, and every finding explains itself.
Goosy reads the changed lines and the code that calls them. Deep Scan covers the whole repository on demand or on a daily schedule.
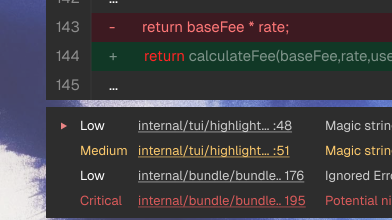
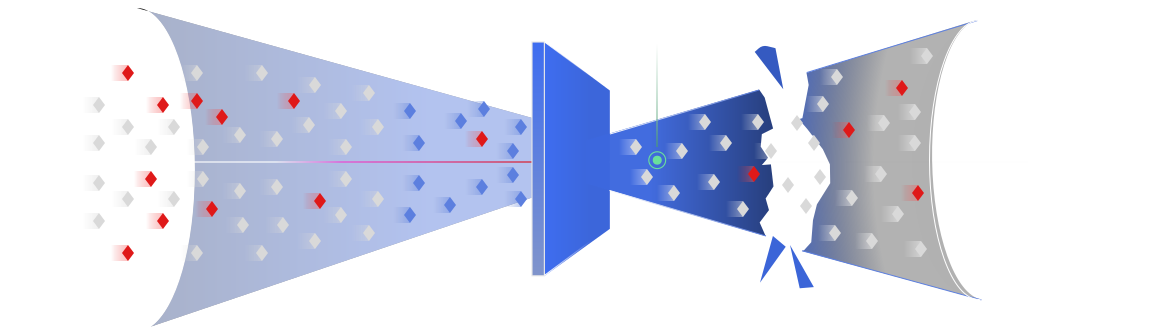
Rule-based analysis and an AI review both read every change. Goosy merges them and removes duplicates.
Goosy checks whether flagged code can be reached from an entry point. Findings it can show are unreachable never make the report.
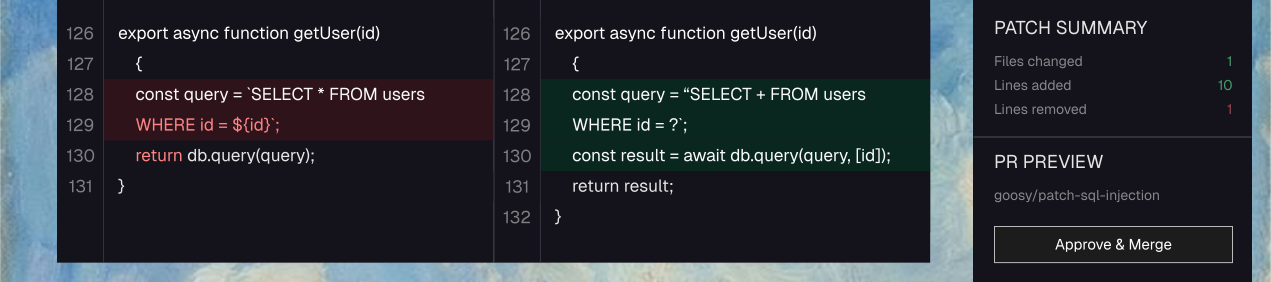
Fixes arrive as patches you can review. Apply one, or use Fix all on a pull request. Auto-push stays off until you turn it on for a repo.
Scans run as background jobs. You get a scan ID straight away and can check progress at any time.
GitHub access is scoped per organization through the Goosy GitHub App. API and MCP tokens can expire, and you can revoke them at any time.
■ SURFACES
Connect a repo once. The CLI and MCP server check your code before you push. The dashboard shows results for the whole team.
Goosy reads each change along with the code around it. It posts a summary and inline comments on changed lines. Fixes arrive as diffs you approve.
installgithub.com/apps/goosy-prod-bot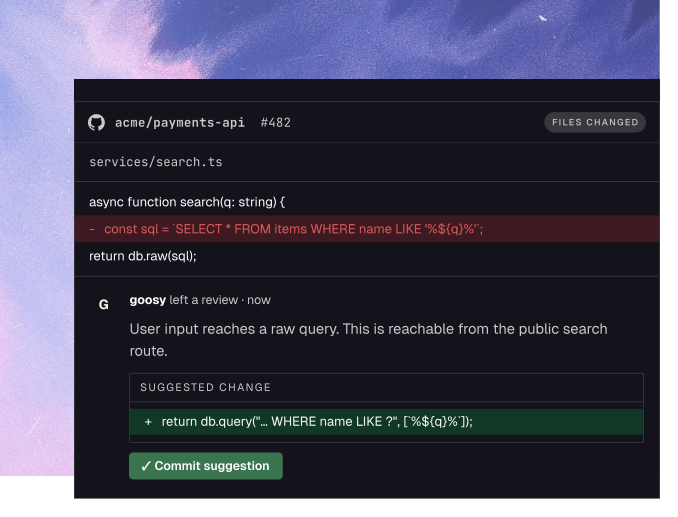
Scan your code before you push, or run the scan in CI. Set a minimum severity and the command exits non-zero when a finding meets it.
$ npm install -g @goosyai/goosy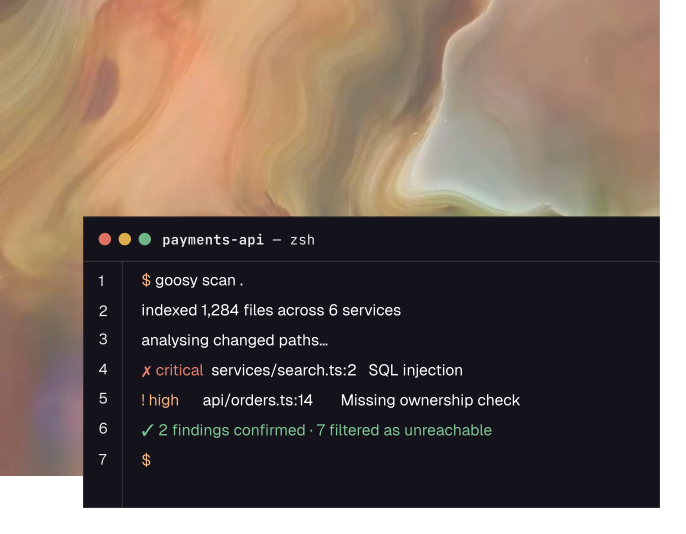
Goosy runs as an MCP server. Clients such as Claude Code, Cursor and VS Code scan the code the agent writes and get findings and fix diffs back.
$ claude mcp add goosy -- npx -y goosy-mcp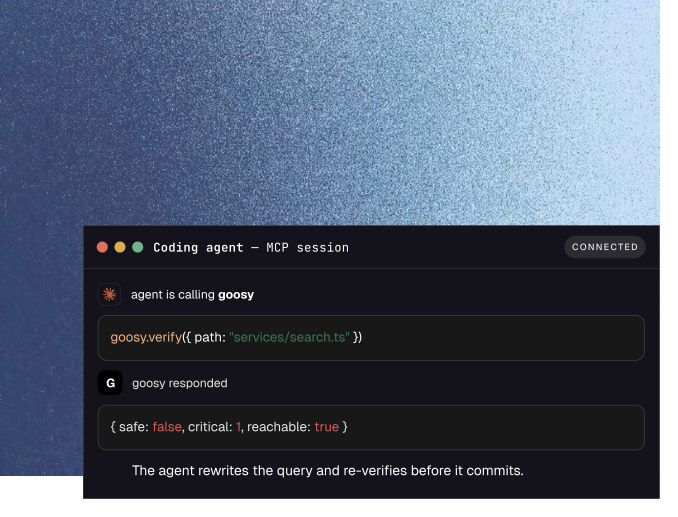
See open findings and past scans for every connected repo, in one view.
Open dashboard →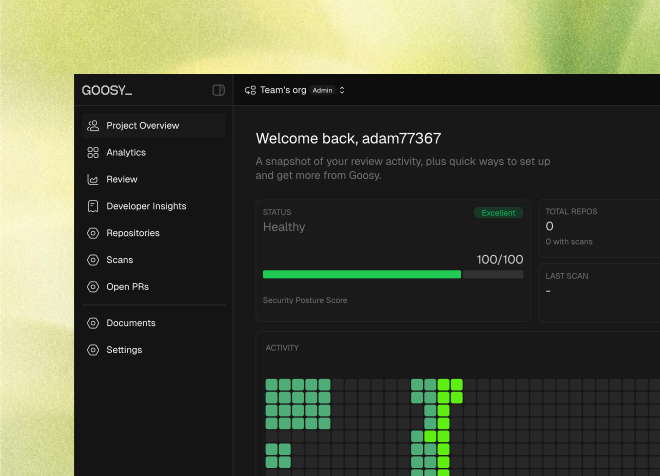
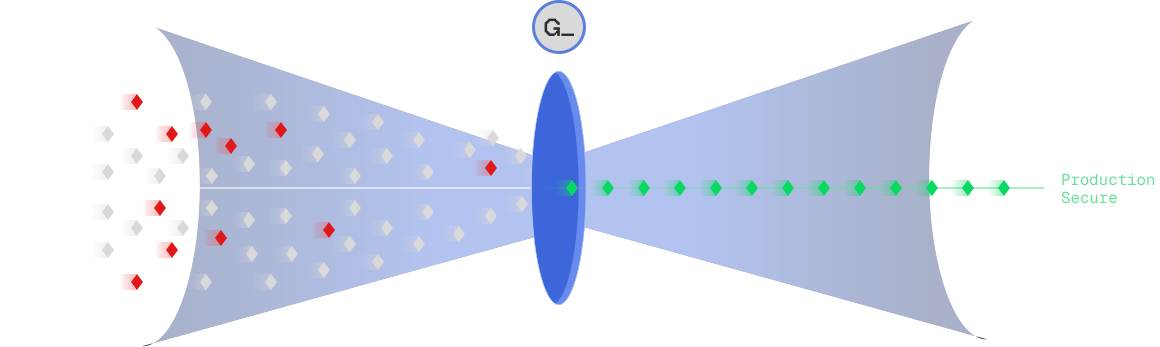
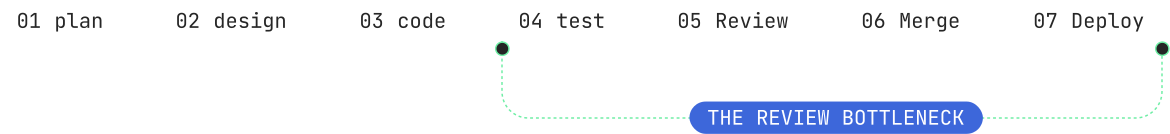
Plan, code, test, review, merge, deploy. Every change must pass
review before it merges.
WHAT WE CATCH
Rule-based analysis and an AI review both read your code.
Two checks, one report. Goosy removes duplicates and explains every finding.
Anything a caller controls, from a query param to an uploaded file,
traced to the point where the app uses it.
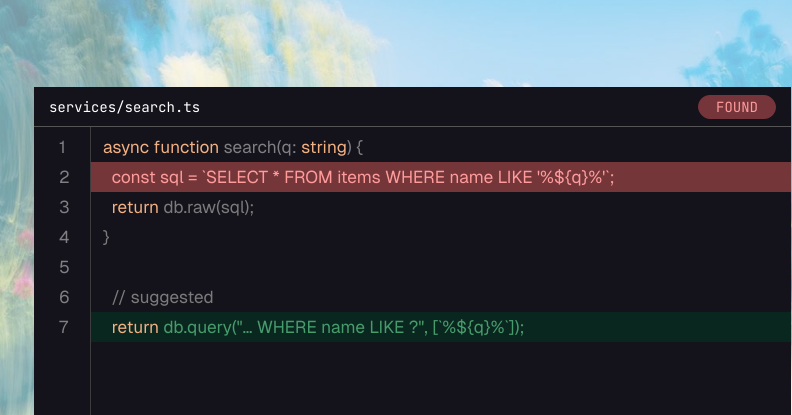
Deep Scan has a dedicated SQL injection detector. Candidates are cross-checked before they reach you.
Tests pass, because the code works exactly as written for
a user who should never have been allowed in.
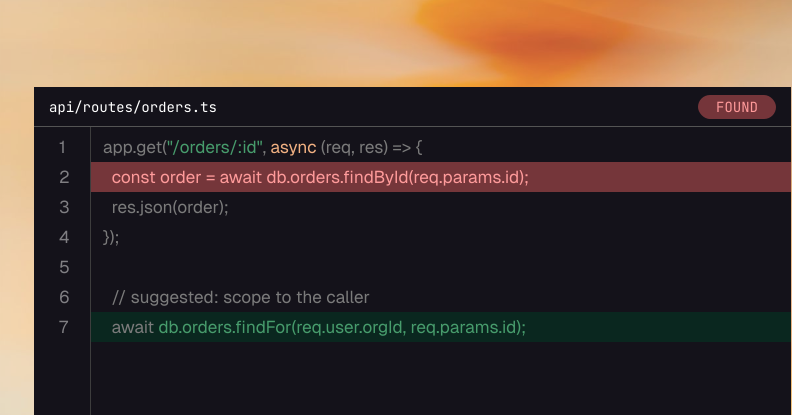
Goosy reads the callers of changed code, so it can see whether a check runs before the sensitive call.
Keys committed to source, passwords hashed with a broken algorithm,
randomness anyone can predict.
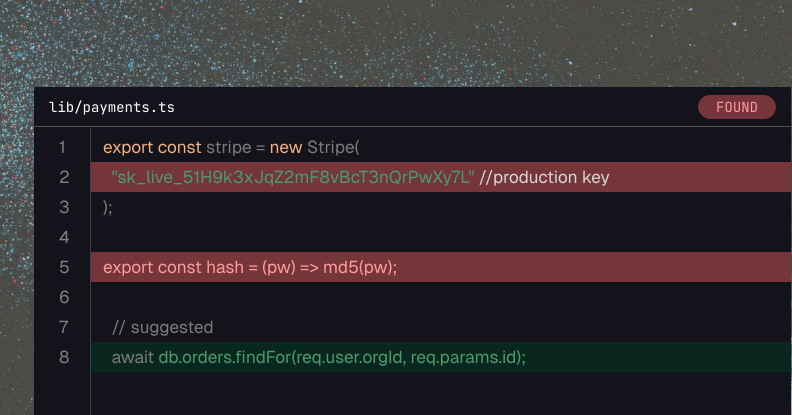
Deleting the line leaves the key in git history. Rotate the key.
Each one is minor on its own.
Together they turn an incident into a breach.
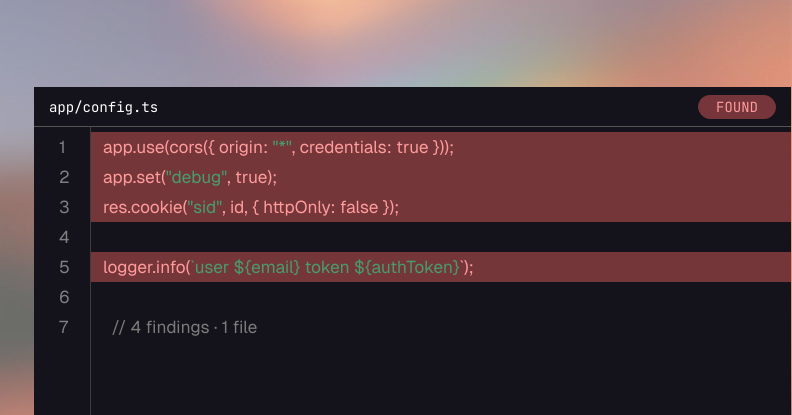
Each finding names the exact lines and explains the impact.
Races, leaks and memory faults. They often survive code review, because
they depend on timing or on code outside the diff.
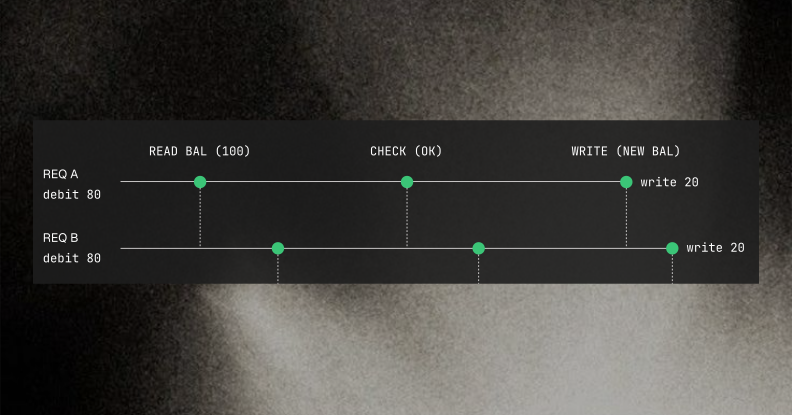
Goosy looks for the exact order of operations that triggers each race.
Logic that looks right line by line, but lets a request skip a check,
run steps out of order, or reach data it should not see.
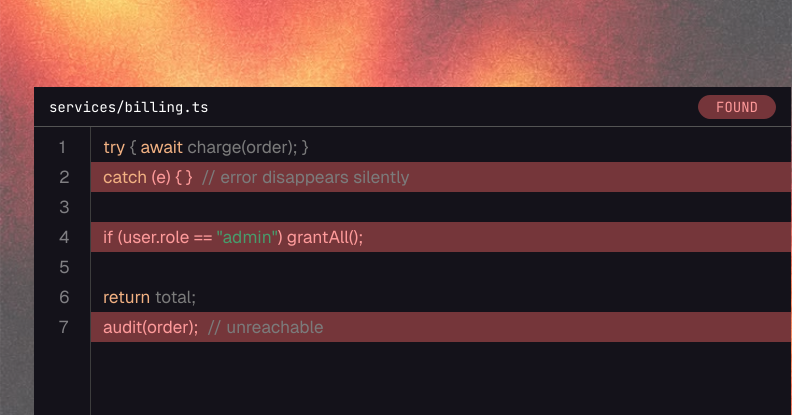
Goosy reports logic bugs in their own category, apart from security findings.